
Building Vietnam’s digital future: Trustworthy agentic AI in 2026

2026 is the year AI moves from speculation to real-world deployment and value. Yet a global industry forecast predicts 40 per cent of agentic AI projects will be cancelled by the end of 2027, due to escalating costs, unclear business value or inadequate risk controls. It suggests better advice and an ecosystem of support are needed to make agentic projects a success, which must include addressing new security considerations.
There are early signs that the rise of agentic AI is transforming how organisations operate. In retail, AI agents are already managing inventory, optimising pricing, assisting customers, forecasting demand, and driving intelligent operations across complex supply chain decisions.
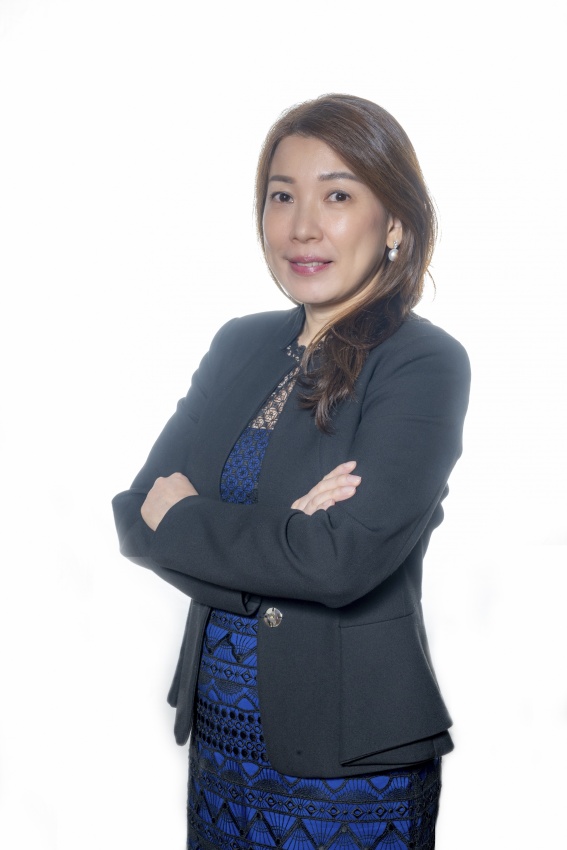 |
| Kym Lim, acting country manager, Vietnam, Zebra Technologies. Photo: Zebra Technologies |
At the same time, logistics organisations are deploying autonomous agents to coordinate warehouse operations, route shipments, manage fleet utilisation, track inventory movement, and resolve operational exceptions in real time.
These systems are no longer simple chatbots or assistants - they are becoming autonomous digital operators capable of making decisions and executing actions across business-critical systems.
These developments are particularly relevant in Vietnam, where rapid growth in e-commerce and logistics is accelerating digital transformation across both sectors. Vietnam’s e-commerce market expanded 22 per cent on-year in the first nine months of 2026, with third-quarter growth accelerating to 27 per cent.
As retailers and logistics providers connect more applications and data systems to streamline commerce, inventory management and delivery operations, real-time asset visibility and trusted, secure interactions between AI agents and core business platforms will be increasingly critical to protecting Vietnam’s position as a rising global supply chain hub.
New security considerations in 2026
While the business benefits are significant, the security implications are equally profound. As AI agents gain access to enterprise applications, APIs (Application Programming Interfaces), devices, customer information, and operational systems, organisations must address a critical question: How do we secure AI agents that increasingly operate like employees but at machine speed and scale?
Traditional AI security concerns such as prompt injection, data leakage, and model vulnerabilities remain important. However, security leaders are now confronting a broader challenge – governing autonomous agents that can access tools, execute workflows, interact with physical devices, and influence business outcomes without constant human oversight. This challenge is no longer just operational; it is regulatory.
With the enactment of Vietnam’s landmark Law on AI in March 2026, the conversation has officially shifted from voluntary model security to legally mandated digital workforce governance. Securing these autonomous workforces requires a fundamental shift in how we approach enterprise trust.
Treat AI agents as digital identities
Every AI agent should be managed as a non-human identity rather than merely an application. Just as organisations govern employee access through identity and access management systems, AI agents require unique credentials, role-based permissions, lifecycle management, and continuous auditing.
In retail, an inventory optimisation agent should not automatically gain access to customer payment systems. In logistics, a route-planning agent should not be able to modify warehouse management configurations without authorisation. Applying least-privilege principles ensures that agents can perform their intended tasks while minimising security exposure.
Furthermore, under Article 4 of Vietnam's AI framework, human control must remain the final arbiter over critical decisions. Implementing secure identity boundaries ensures autonomous agents operate as compliant, highly coordinated assistants rather than unmanaged liabilities. Without proper governance, an unmanaged AI agent can quickly become a highly privileged insider capable of accessing sensitive systems and data.
Govern MCP and tool access
The Model Context Protocol (MCP) is emerging as a key mechanism for connecting AI agents with enterprise tools, databases, applications, and external services. While this connectivity enables powerful automation, it also expands the attack surface.
Organisations should establish strong governance around MCP servers and tool integrations. This includes validating trusted MCP endpoints, implementing allow lists for approved tools, inspecting contextual information passed to models, and continuously monitoring tool usage.
For retailers, this could mean restricting access to pricing engines, loyalty systems, or inventory platforms. For logistics providers, it may involve controlling access to transportation management systems, warehouse automation platforms, carrier networks, and shipment tracking services. A compromised tool connection can provide attackers with a direct path into critical operational workflows.
Secure runtime operations
Security cannot stop once an AI agent is deployed. Autonomous systems must be monitored continuously throughout their operational lifecycle.
Runtime security controls should include policy enforcement, behavioural monitoring, approval checkpoints for high-risk actions, anomaly detection, and emergency kill switches. These controls help identify and contain risky behaviour before it impacts business operations.
For example, a retail agent that suddenly attempts to modify thousands of product prices should trigger investigation. Similarly, a logistics agent that begins rerouting large volumes of shipments or altering delivery schedules outside established policies should be flagged immediately.
Continuous runtime visibility is essential because even well-trained agents can drift from expected behaviour due to changing inputs, evolving objectives, or malicious manipulation. Under the new regulatory environment, establishing these safeguards isn't just about operational safety; should a serious operational anomaly or data security incident occur, swift technical intervention and reporting through Vietnam's National Single-Window AI Portal are expected.
Don't forget the devices
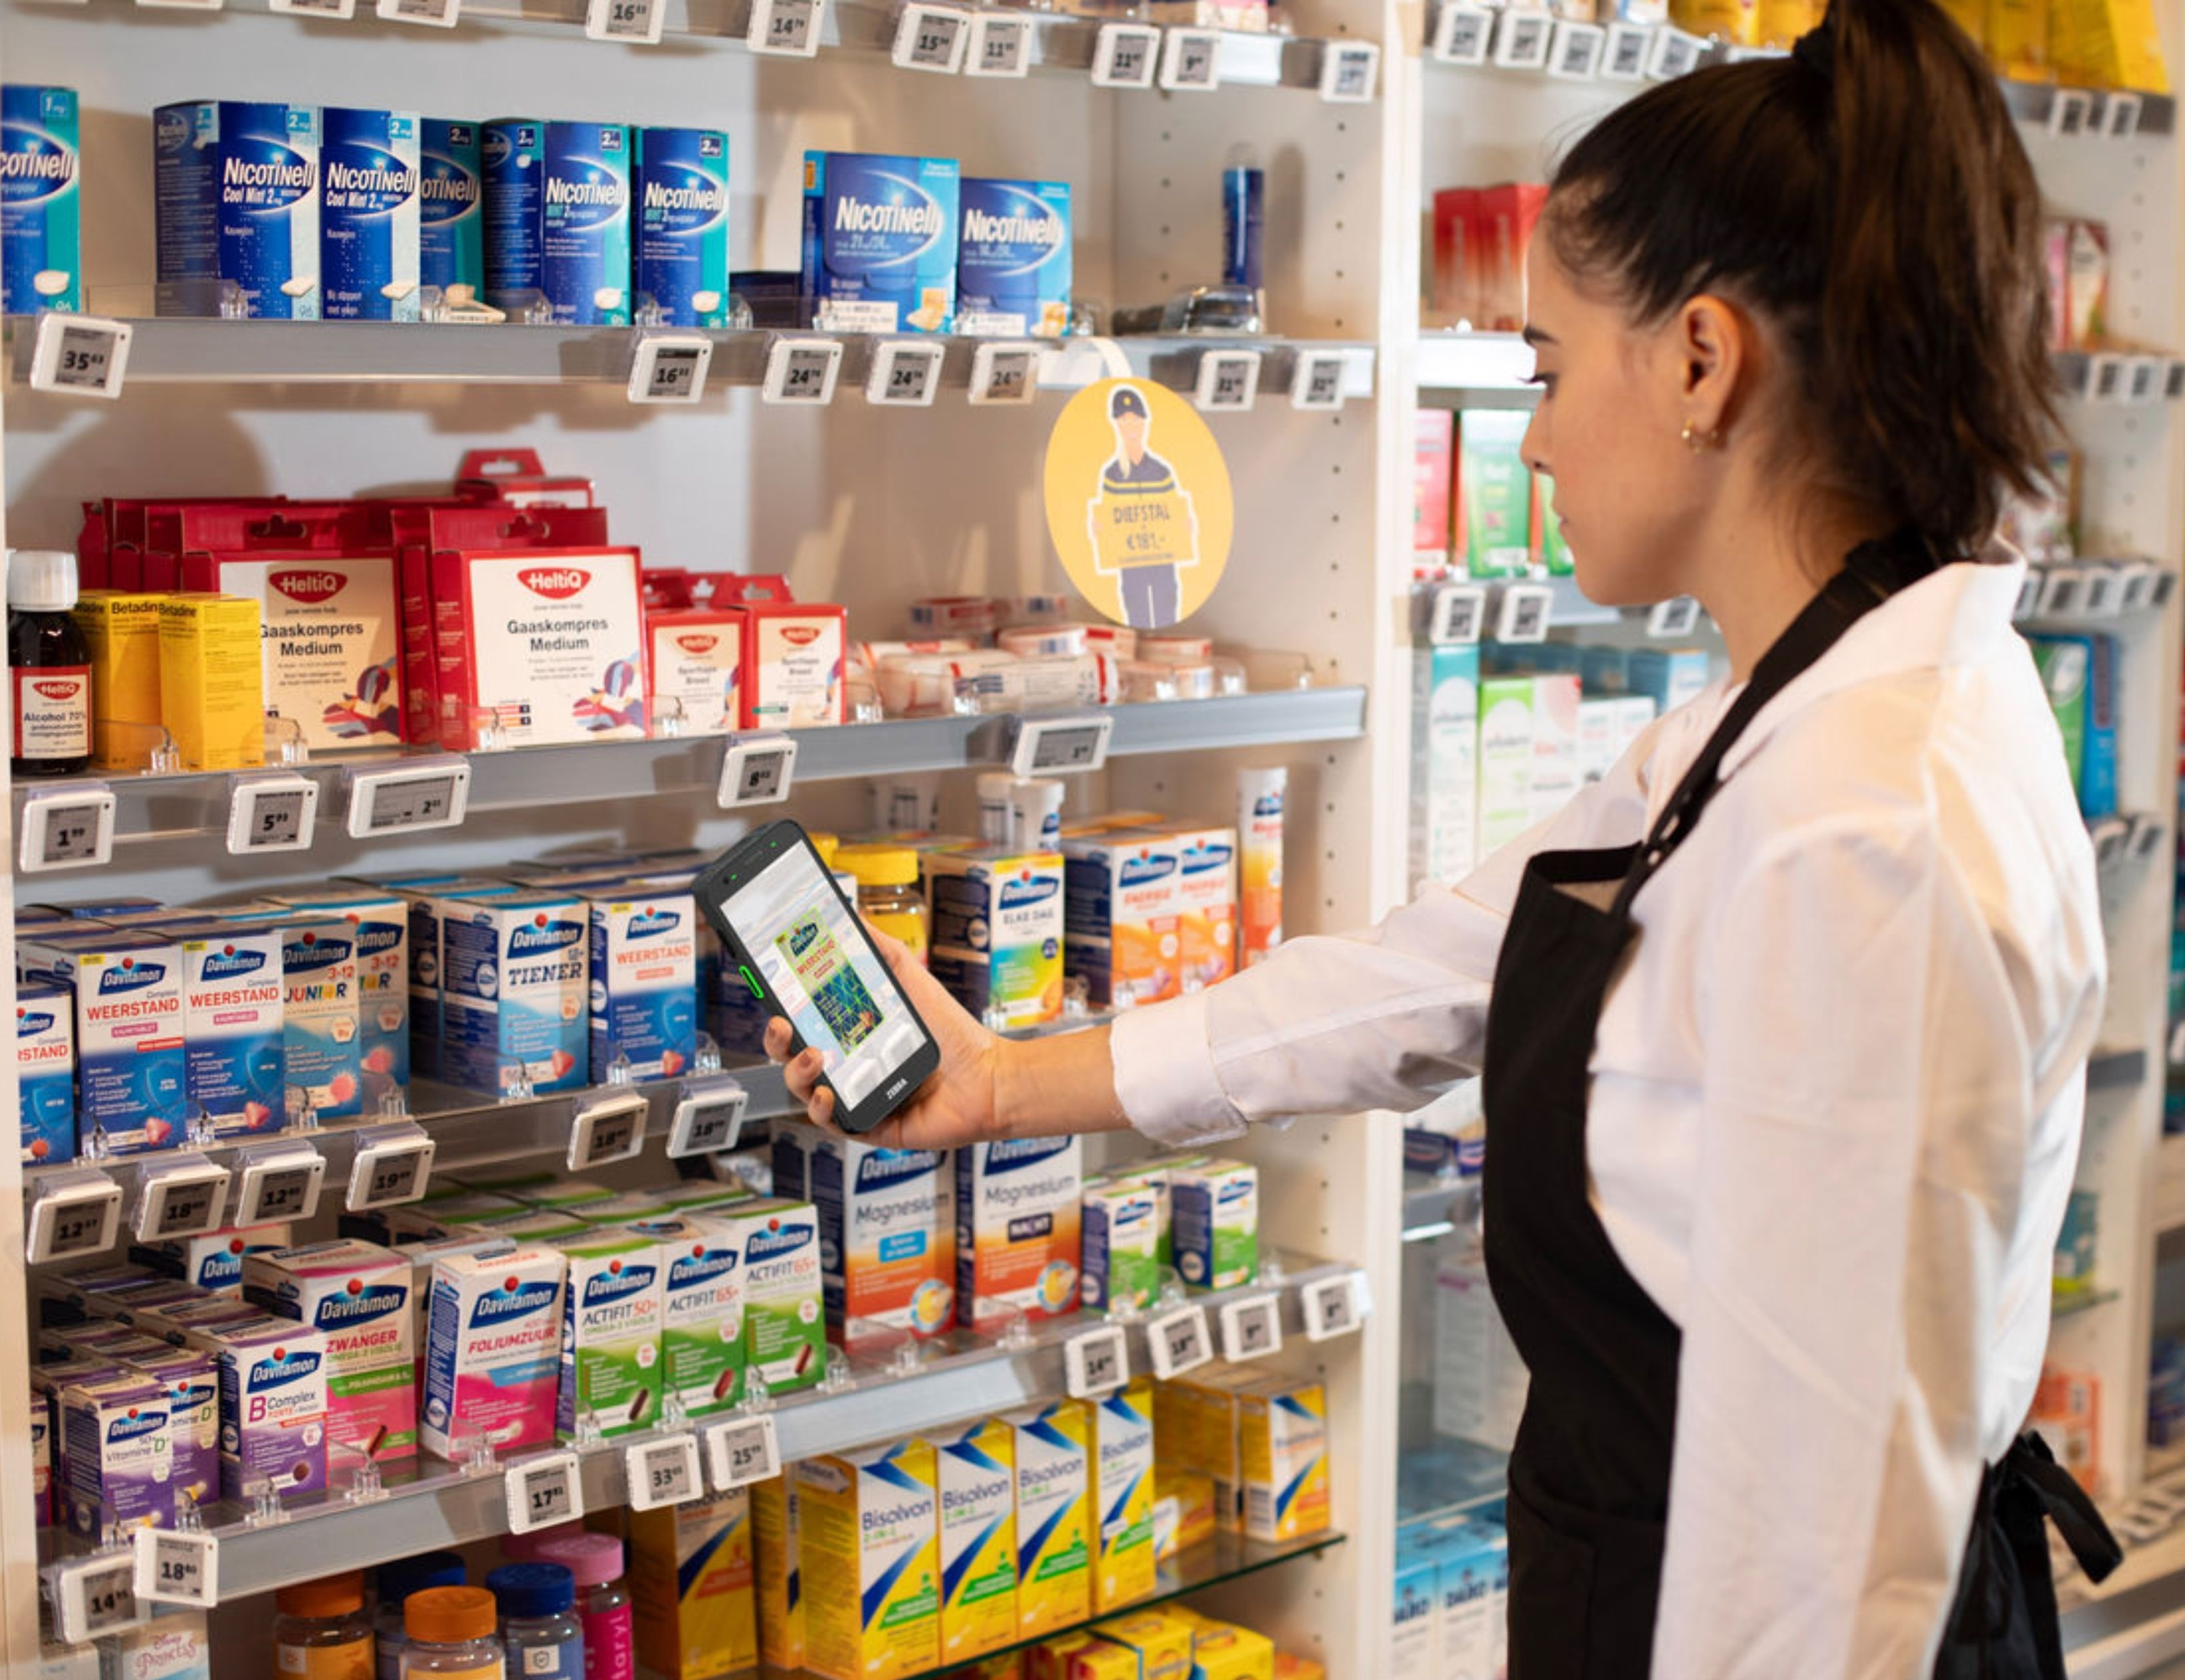
Agentic AI increasingly interacts with physical infrastructure. In retail environments, agents may access point-of-sale systems, kiosks, handheld scanners, smart shelves, and IoT devices. In logistics operations, agents often interact with warehouse scanners, robotics systems, automated storage equipment, vehicle telematics, fleet management platforms, and industrial IoT sensors that empower the connected frontline.
A compromised endpoint can distort real-time asset visibility and influence the decisions made by an AI agent, creating downstream business risks. In short, device trust is the foundation of agentic trust. Device posture validation, endpoint security, and continuous compliance monitoring should therefore be integrated from day one into any Agentic AI security strategy.
Build security across every layer
Organisations should adopt a layered security approach spanning agent identities, MCP and tool governance, runtime protection, endpoint trust, API security, and data protection. Strong authentication, least-privilege access, token management, behavioural analytics, and continuous monitoring should work together to provide defence in depth.
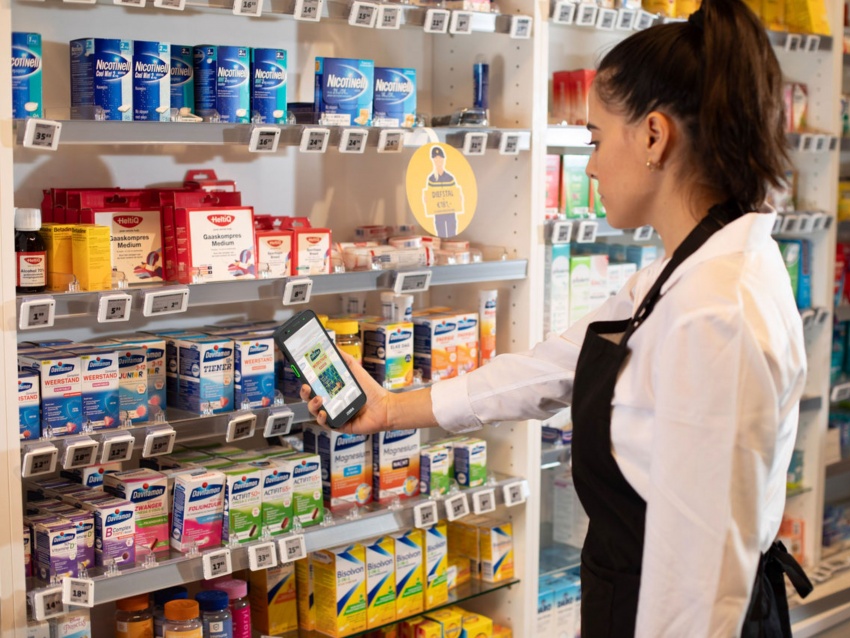 |
| Photo: Zebra Technologies |
Continuously red team your agents
Traditional penetration testing is no longer sufficient. Agentic AI systems must be continuously evaluated against threats such as prompt injection, goal hijacking, privilege escalation, tool abuse, workflow manipulation, and business logic attacks. Retail and logistics organisations should regularly test complete agent workflows rather than individual components.
The objective is to understand how autonomous systems behave under real-world adversarial conditions and identify weaknesses before attackers do.
Getting the balance right
Retail and logistics organisations are rapidly deploying AI agents to automate increasingly critical business processes. The leaders in this new era are not those who deploy the most intelligent agents, but those that also establish the strongest foundations of trust, governance, and security.
As AI agents gain access to inventory systems, pricing engines, warehouse platforms, transportation networks, customer data, and operational devices, the key question will be getting the balance right between securing AI agents like software and governing them as digital identities.
By bridging intelligent operations with a secure, connected frontline, Vietnamese enterprises can confidently turn AI potential into real-world performance.
What the stars mean:
★ Poor ★ ★ Promising ★★★ Good ★★★★ Very good ★★★★★ Exceptional
 Tag:
Themes: Digital Transformation
- Building Vietnam’s digital future: Trustworthy agentic AI in 2026
- Vietnam accelerates 5G utilisation and prepares for 6G
- Vietnam strengthens inter-regional cooperation on enhancing AI capabilities
- Science and tech funding disbursement set to accelerate
- Vietnam transforming AI ambitions into business impact
Related Contents


Latest News
More News
- Average startup capital per new business doubled to $800,000 (November 05, 2026 | 11:56)
- Vietnam’s trade turnover surpasses $1 trillion for the first time (November 05, 2026 | 11:50)
- New customs framework to reward compliance and target risks (November 04, 2026 | 16:59)
- Vietnamese brands make gains in ASEAN’s brand economy (November 03, 2026 | 16:54)
- Lite-On to pump additional $320 million into subsidiaries in Vietnam (November 02, 2026 | 17:19)
- Local firms need bigger role in global supply chains, panel hears (November 02, 2026 | 14:03)
- SABECO posts stronger earnings ahead of Lunar New Year peak (November 02, 2026 | 14:01)
- FV reaches 100 Da Vinci Xi robotic surgeries attracting international patients to Vietnam (October 29, 2026 | 19:00)
- Robots no longer preserve of large corporations (October 29, 2026 | 15:35)
- Vietnam moves closer to 10 per cent growth target (October 28, 2026 | 12:48)


 Mobile Version